PRACTITIONER LEADERSHIP & EXECUTIVE ADVISORY

Cybersecurity Leadership & Professional Expertise

BlueRanger Info-Sec combines decades of enterprise security engineering, institutional risk governance, and hands-on systems architecture to help organizations build resilient, audit-ready security operations.

Meet Our Leaders Schedule Discovery Call
OUR EXPERTS

Meet the Leadership Team

Direct access to senior cybersecurity professionals with verified global enterprise backgrounds and proven technical credentials.

Rishi Kant - Cybersecurity, GRC & AI Security Expert at BlueRanger Info-Sec
EXECUTIVE ADVISOR & SECURITY ARCHITECT

Rishi Kant

Cybersecurity, GRC & AI Security Expert

CISSPCISMCIPMCCSPOSCPGenAICRISCCEHISO

Information security professional whose background spans executive cybersecurity leadership, enterprise security architecture, governance, risk management (GRC), and cloud defense across international financial services and technology companies.

Key Advisory Domains

  • Enterprise Security Strategy & Board Risk Reporting
  • ISO/IEC 27001, NIS2 & DORA Regulatory Readiness
  • Cloud & Application Security Architecture (AWS/Azure)
  • Responsible AI Governance & Modern Threat Modelling
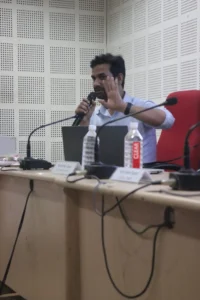
Nadeem Ansari - Founder & Lead Technical Instructor at BlueRanger Info-Sec
FOUNDER & LEAD TECHNICAL TRAINER

Nadeem Ansari

Founder & Technical Systems Lead

MCSE (Microsoft Certified Systems Engineer)Certified Ethical Hacker & Web Security SpecialistPerformance Systems & Ad Architecture Specialist

Founder and lead technical instructor of BlueRanger Info-Sec with 14+ years of hands-on industry exposure managing international digital marketing systems, IT infrastructure, and web security projects for clients across the USA, UK, and Dubai.

Key Practice Domains

  • 14+ Years Global Digital & Infrastructure Delivery
  • Enterprise Systems Engineering (Microsoft Transcript Verified)
  • Practical Cyber Defense & OWASP Web Security Training
  • Workshops at RSMT, Integral Univ & Udai Pratap College
ℹ️

Professional Background & Affiliation Transparency

Professional backgrounds and historical career milestones reflect the individual professional records of our team members. Prior employers and corporate affiliations (such as Mastercard, Sumitomo Mitsui Trust Bank, ESW, IBM, etc.) represent past and present employment or independent non-profit board governance positions. They do not constitute client engagements, corporate sponsorships, endorsements, or business partnerships with BlueRanger Info-Sec.

ENGAGEMENT PHILOSOPHY

How Our Advisory Model Works

We bridge executive board-level governance with hands-on technical architecture to deliver measurable security outcomes.

01

Direct Practitioner Access

Engage directly with senior professionals who have engineered systems, directed security programmes, and responded to real-world incidents, not junior account managers.

02

Evidence-Based & Unbiased

We operate independently of hardware and software vendors. Our architectural recommendations are based solely on your specific threat model, budget, and regulatory profile.

03

International Standards Rigor

Every review aligns with internationally recognized standards—ISO 27001, NIST CSF, GDPR, NIS2, DORA, and OWASP—providing your stakeholders with defendable governance evidence.

04

Pragmatic Business Alignment

We understand that security must enable business velocity. Our remediation roadmaps are prioritized by business risk, engineering practicality, and cost-efficiency.

Discuss Your Security Requirements With Our Experts

Whether you are preparing for an ISO 27001 audit, assessing your cloud security posture, or evaluating your AI risk controls, schedule a confidential preliminary consultation today.

Request Consultation Explore Consulting Services